 DoNotLeak
For executives
Your teams already use AI. Do you know what they give it?
AI has become a leadership issue: staying current means not leaving the lead to those who use it well — and banning it does not stop it. But every text pasted into a personal account leaves with no contract and no trace, and a leak is paid for first in trust. Here: what is at stake for the organisation, your order of magnitude, and what is yours to decide.
What is at stake
An advantage to take, a leak to prevent.
Your teams have not waited: to write, summarise and translate, they already use AI assistants — often a free tool, opened with a personal account, that the organisation did not choose. That is Shadow AI: a proposal, a spreadsheet, a client’s email then leave on a path the company does not see.
- 78%
- of AI users bring their own AI tools to work (31,000 people surveyed in 31 countries).Microsoft and LinkedIn, 2024 Work Trend Index
- 72%
- of the employees who routinely use AI services on a work device do so with an account tied to a non-corporate email.Verizon, 2025 Data Breach Investigations Report
Why doesn’t the company see it?
Nobody does it to cause harm: a deadline, a tool that really helps, an approved tool that is missing or slower. The risk is invisible at the moment of the gesture — and the day it shows, your clients’ trust is at stake, even before the legal question.
- Outside any contract
No agreement binds the provider to the company: the terms are the ones the employee accepted, for themselves.
- Outside any log
The company does not know what left, when, or to which service — so it can neither answer for it nor correct it.
- Outside any policy
Whatever the charter says about what may be shared, it is not there at the moment of the paste.
Your order of magnitude
One paste is small. A year of them is not.
One paste looks harmless. Multiply it by the working days of a year, then by the people of a department, then by the departments of a company: that total is what the organisation exposes — and no one sees it, because no one sends it at once. An order of magnitude to put before the executive committee, not a measurement.
Your figures
Everyone who writes, sends or pastes documents.From 1 to 100,000 · default 250
Never more than the organisation.From 1 to 10,000 · default 12
An email with its attachment, a file shared with a supplier, a text pasted into an assistant.From 0 to 50 · default 5
The three documents of the showcase carry four or five each.From 1 to 50 · default 4
What can leave
Sensitive items sent outside, counted each time they leave.
Your department
- per day
- 24
- per month
- 440
- per year
- 5,280
The whole organisation
- per day
- 500
- per month
- 9,167
- per year
- 110,000
Occurrences, not distinct people: the same client counts again in every document that names them. How it is computed is explained below.
Computed in your browser — nothing you enter is sent.
The page arrives showing the defaults; from then on, every figure is computed by the page itself, in your browser. Moving a slider sends no request: open your browser’s network tab and watch. An automated test checks exactly that — zero requests while the inputs move.
The link carries your figures after the # sign, the part of an address a browser never sends to a server. Whoever opens it recomputes the same figures in their own browser.
The page keeps nothing: your figures live in the address itself.
Your figures, multiplied — nothing hidden.
No hidden coefficient: the department’s figures are this product; the organisation’s are the same product with its whole headcount. Each assumption is written below — so you can answer whoever asks where the figure comes from.
12people in the department×5documents a day, each×10%carry sensitive data×4items in each=24items a day
24items a day×220working days a year=5,280items a year
220 working days a year
Five days a week, minus five weeks of leave and the public holidays: about 220 days. A month is a twelfth of that year — about 18 working days.
Occurrences, not distinct items
The same client appears in many documents: their name leaves with the quote, the contract, the invoice and the follow-up email. The figures count every time an item leaves. How many distinct people or records that makes depends on your files, and five figures cannot tell — so the page invents no ratio and shows none. Each occurrence is still one more copy outside.
An order of magnitude, not a measurement
The result is built from your own figures; the defaults are a starting point, not a statistic. It pictures a volume — nobody has counted your organisation’s documents, and neither has this page.
Behind the count, duties — and ceilings.
Three frames apply when personal or confidential data leaves — and the organisation answers for it. None of them turns your figures into an amount.
GDPR fines: ceilings, not prices
Up to €10 million or, for a company, 2% of its total worldwide annual turnover of the preceding financial year, whichever is higher — for failing the controller’s obligations, security and breach notification among them (Article 83(4)). Up to €20 million or 4% for breaching the basic principles, people’s rights or the rules on transfers outside the EU (Article 83(5)). The authority sets each fine case by case, weighing among other things the gravity and duration of the infringement and the number of people affected (Article 83(2)). A ceiling is not a forecast: this page computes no fine.
A breach is notified within 72 hours
A breach of security leading to the unauthorised disclosure of personal data is a personal data breach (Article 4(12)); whether a given disclosure is one is assessed case by case. The controller notifies the supervisory authority without undue delay and, where feasible, within 72 hours of becoming aware of it, unless the breach is unlikely to result in a risk to people (Article 33). When it is likely to result in a high risk to them, the people concerned are told as well, without undue delay (Article 34).
Contracts: the confidentiality clause
Client files often come under a confidentiality clause or a non-disclosure agreement. Disclosing a trade secret without its holder’s consent, in breach of such an agreement, is unlawful under the EU Trade Secrets Directive (Article 4(3)). What that costs is written in each contract and settled case by case: there is no public figure, so none is shown here.
Directive (EU) 2016/943 (trade secrets), Article 4 — EUR-Lex
What leaves — your know-how
Your edge leaves with the text.
A proposal carries a pricing structure and a method. Source code carries years of engineering. A strategy note carries next year’s choices. Pasted to be summarised or corrected, each hands a copy of the company’s know-how to a provider — and since the original stays in place, nobody notices.
Protecting a secret starts with keeping it
EU law protects a trade secret only if its holder has taken reasonable steps to keep it secret.
An honest limit
A strategy, a margin or a manufacturing process can be confidential without containing a single name, email or number. DoNotLeak finds personal data, identifiers and access keys; it does not recognise a secret by its meaning. Reading before sending stays with you.
What leaves — contracts and tenders
A confidentiality clause, breached without anyone deciding it.
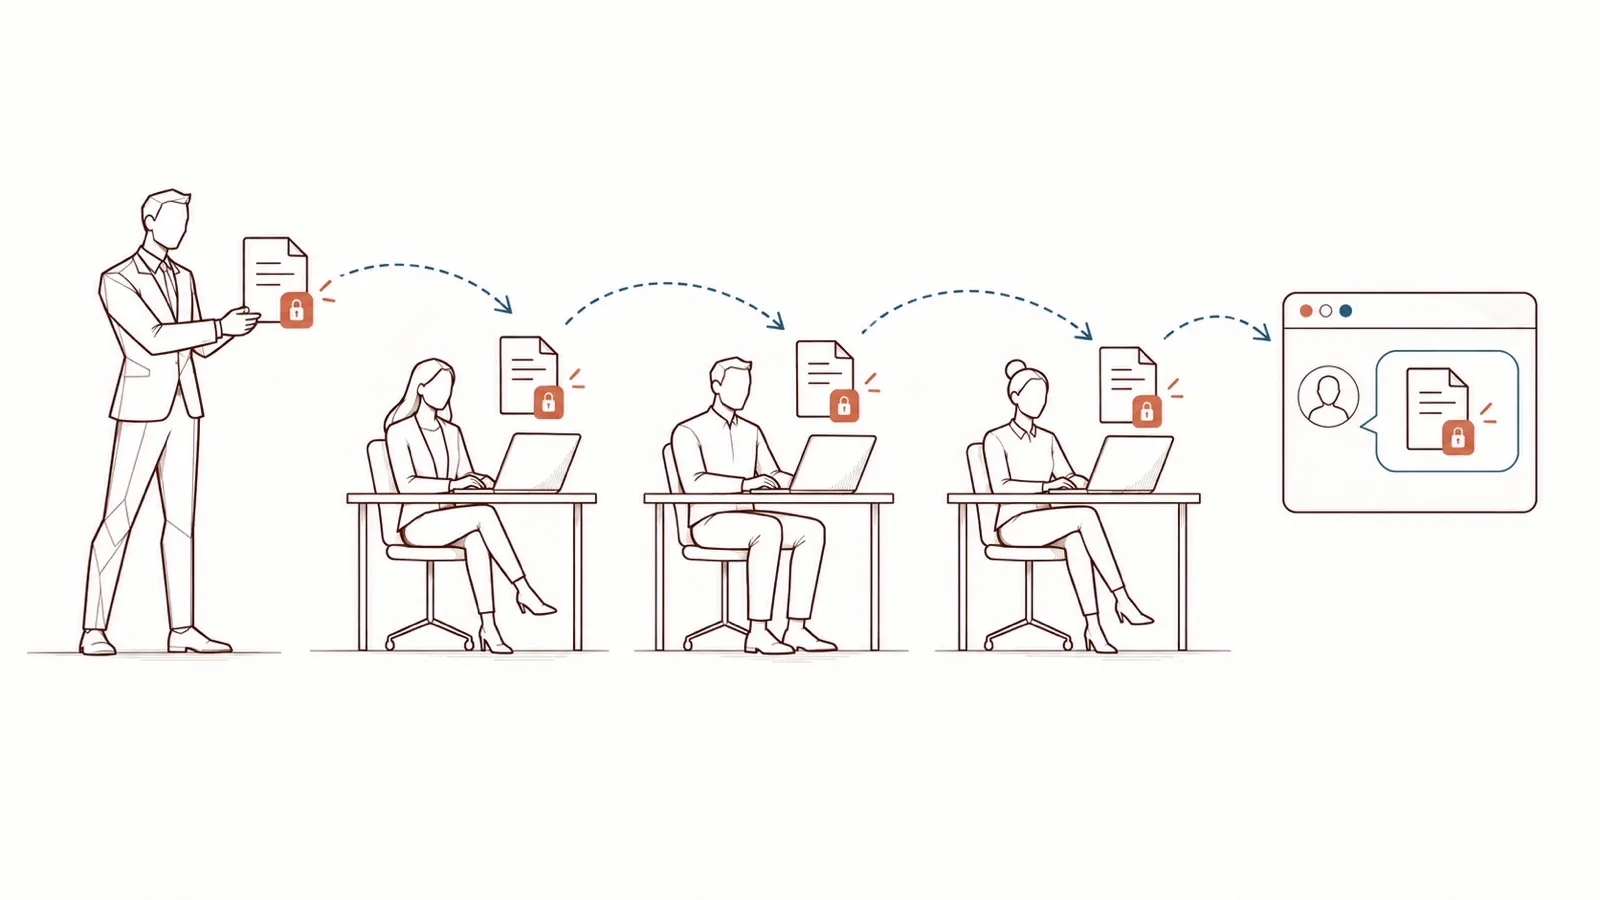
Tender documents, a proposal under a non-disclosure agreement, a client’s file, a supplier’s price list: most were entrusted to the company on condition that they stay within it, or reach only named recipients.
Pasting them into an AI service hands them to a third party. Nobody decided to breach the clause; a paste did. Whether a given clause is breached depends on its wording — a question for your legal team.
What leaves — your clients’ trust
Their data, your responsibility.
Clients, patients, candidates, colleagues: a pasted text is often about people. The GDPR does not forbid AI; it asks the organisation to answer for what happens to their data.
European customers write data protection into their contracts with suppliers: who may process their data, where, under which safeguards. A paste into a personal account answers none of those questions.
The organisation answers for it
The controller — the company, not the employee, not the DPO — must put appropriate measures in place and be able to demonstrate them.
GDPR, Articles 5(2) and 24
A contract with every processor
A provider processing personal data for the company must be bound by a contract that sets its obligations. An account an employee opened for themselves is no such contract.
GDPR, Article 28
Transfers outside the EU
Many AI services are run from outside the European Union. Sending personal data there falls under the GDPR’s transfer rules: an adequacy decision or appropriate safeguards, for instance.
GDPR, Chapter V (Articles 44–49)
Security, and fine ceilings
The controller must secure the data it processes. Infringing the core principles or the transfer rules can be fined up to €20 million or 4% of worldwide annual turnover, whichever is higher. These are ceilings, not prices: the authority sets each fine case by case.
GDPR, Articles 32, 83(2) and 83(5)
This page explains; it is not legal advice. Each contract and each processing deserves a reading by your legal team or your DPO.
What leaves — your access
Material for a later attack.
A snippet sent for debugging, a configuration pasted to ask a question: what helps today can open a door tomorrow.
- 94 days
- the median time to fix secrets found leaked in a GitHub repository. Credential abuse remains the most common known way into a breach.Verizon, 2025 Data Breach Investigations Report
A credential
An API key, a token, a password, a connection string left in a snippet: whoever reads it can use it.
An internal hostname
The name of a server, an address on the internal network: a map of what exists, and where.
An architecture note
Which components, which versions, how they connect: the reconnaissance an attacker would otherwise have to do.
What DoNotLeak spots here
Keys and tokens in common formats, private keys, connection strings, passwords written after a label, IPv4 addresses. A server’s name or an architecture note, it does not recognise.
Once it has left
A text sent cannot be recalled: five steps, out of your hands.
A free account does not automatically mean training. What happens to a text depends on the service, its terms and its settings — and each step is a separate question.
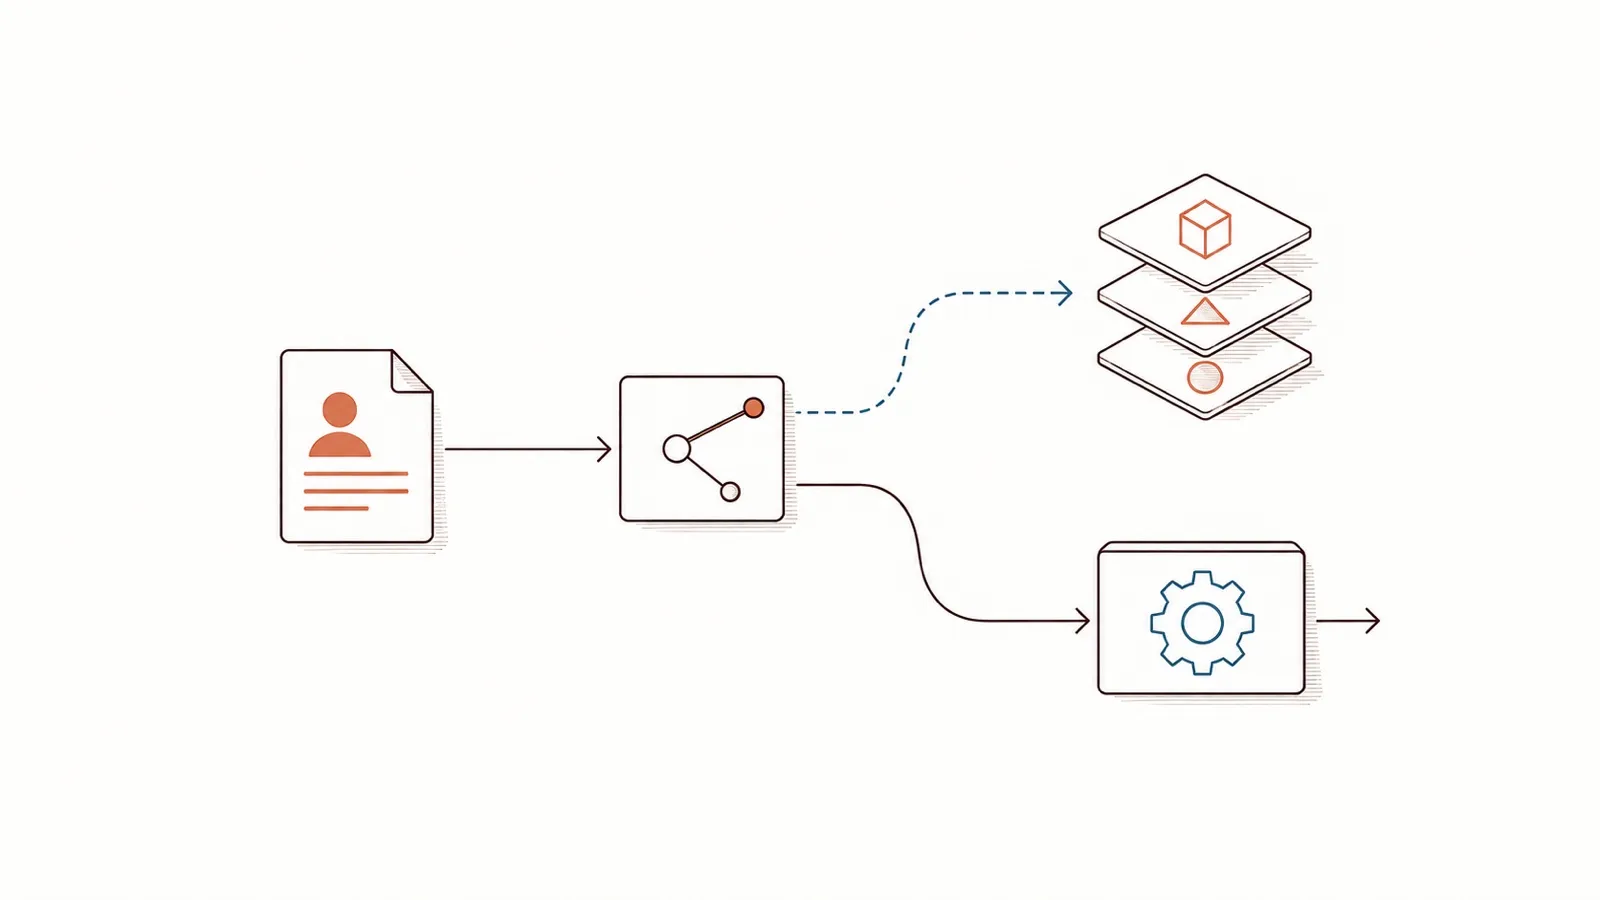
Exposure
The text reaches the provider’s servers. From there on, it is out of the company’s hands.
Retention
It is kept in the conversation history and in the provider’s logs, for as long as the provider’s terms say.
Training
On some consumer offers, depending on the terms and the settings, conversations can be used to improve the models. The CNIL recommends turning that reuse off.
Memorisation
A model can retain fragments of what it was trained on: researchers extracted verbatim training data — personal data included — from a language model.
Restitution
What a model has retained can, in some cases, resurface in an answer to someone else. The EDPB holds that a model trained on personal data cannot, in all cases, be considered anonymous.
The decision
Frame rather than ban: four decisions.
A ban without a practicable path invites detours. What holds is a frame people understand and a tool within everyone’s reach — which is also what the CNIL recommends: choose the tools, say what may be shared, train the people who use them.
- The frame and the example charter
A frame rather than a ban
A short charter (what may leave, what may not, whom to call), training that builds the reflex, and a procedure known in advance for the day something leaves anyway.
An owner, backed by the leadership
Your DPO has a kit for it: a diagnosis, a 90-day plan and what it takes to roll it out — free, with no form to fill in. What they need from you: approve the charter, name a sponsor, start the 90 days.
In the DPO’s kit, the note to the executive committee: the situation, the risk, the plan, the decision to sign. Download the note (PowerPoint)
The DPO’s plan- Protect a text
A tool within reach
Before every prompt, the person sees what would leave and decides — ten seconds, on the page, with no account. For a team, the same engine can also run on the organisation’s own servers, with its API.
Volumes measured, never people
Count the approved tools, the people trained, the incidents reported: enough to steer. Nobody is watched, and what each person writes is not read.
On a real text
What your teams paste, and what the AI receives.
Personal data is any information about a person who can be identified, directly or by putting pieces together. DoNotLeak looks for two kinds, and replaces them in the version you copy.
Direct identifiers
Email addresses, phone numbers, IBANs and card numbers, postal addresses, dates of birth, national ID and tax numbers, vehicle plates — recognised by their format, country by country.
The names of people, companies, places
Found with lists of real names and the shape of the sentence. Explainable rules: no AI model, no third party called.
What you paste
Call with Julie Marchand, purchasing manager at Transports Berthier in Nantes: she sends the quote from julie.marchand@example.org, mobile 06 39 98 41 27, deposit to FR76 3000 6000 0112 3456 7890 189.
What the AI receives
Call with [[PERSON-1]], purchasing manager at [[ORGANIZATION-1]] in [[LOCATION-1]]: she sends the quote from [[EMAIL-1]], mobile [[PHONE-1]], deposit to [[IBAN-1]].
Replacing is pseudonymising, not anonymising
What remains — a job title, a date, a rare event — can still point to someone, and pseudonymised data is still personal data under the GDPR.
No detection finds everything
That is why the page shows everything it found, and why you read before you send.
The way out
Say yes to AI, with a frame that holds.
Keeping the edge AI gives without exposing the organisation: that is a decision to take. Three questions remain, the ones a leadership team asks first.
Why not simply ban it?
Because a ban gets routed around: your teams already use tools nobody chose. A tool within reach makes the right gesture easier than the detour — without giving up what AI brings.
Does it slow the teams down?
Ten seconds before sending: paste, see what would leave, copy the protected version. No account, no installation.
What does it cost?
To start, nothing: the page is open to everyone, with no account. For the organisation — on your own servers, with the API — the options are settled with Contee: write to us on LinkedIn.
Keep protecting yourself — or your whole organisation.
The page stays open to everyone, with no account. For a team or a company, DoNotLeak can run on your own servers, with its API: write to us.